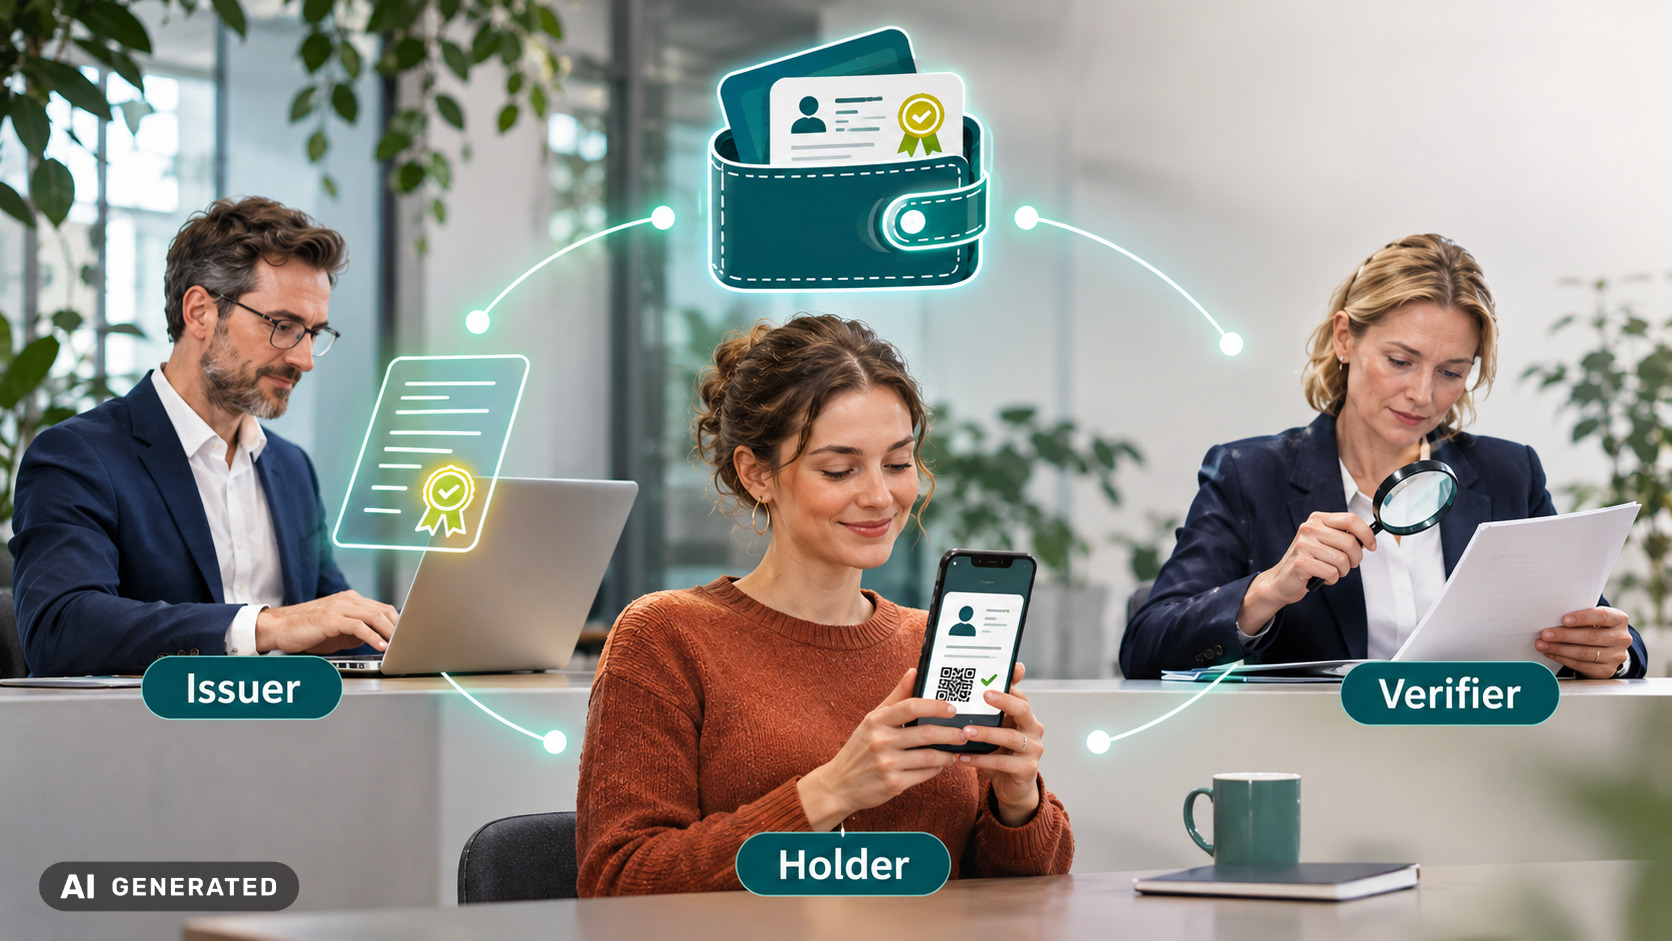
Digital transformation brings with it not only new technologies, but also new roles and responsibilities. Particularly in the context of the EUDI wallet and verifiable credentials, a fundamental question arises for businesses and public authorities: what role do we actually play in this ecosystem?
Whilst technical discussions often revolve around wallets, cryptographic methods and standards, one key aspect is frequently overlooked: an organisation’s role within the wallet ecosystem determines which processes it manages, which data it is responsible for, and what infrastructure it requires. Whether you issue, manage or verify digital certificates, each of these functions entails its own set of requirements that go far beyond the purely technical.
In this article, we explore why defining roles within the wallet ecosystem is so important, what responsibilities are associated with each role, and how you can determine where your organisation stands. Because one thing is clear: without a clear understanding of one’s own role, the implementation of digital identity processes can quickly become confusing or even legally risky.
Many projects in the field of digital identities fail not because of a lack of technology, but because of unclear responsibilities. Who is responsible for issuing digital credentials? Who verifies their authenticity? And who manages them on a day-to-day basis? These questions are not technical details, but strategic decisions that can determine the success or failure of a project.
This is because the role an organisation plays within the wallet ecosystem influences not only the technical architecture, but also compliance requirements, operational processes and even legal liability. A company that issues digital certificates, for example, must ensure that these are forgery-proof and can be revoked if necessary. A public authority that verifies certificates, on the other hand, must establish mechanisms to reliably verify their validity. And a software provider that supplies infrastructure for digital identities must develop multi-tenant solutions that meet the requirements of different customers.
That is precisely why clarifying roles is the first step – even before technical implementation. It helps us ask the right questions: What do we need to do? What are we allowed to do? And what do we need to do that? Without this clarity, organisations run the risk of either investing too much (by building infrastructure they do not need) or too little (by overlooking critical requirements).
The three basic roles: Issuer, Holder, Verifier
The wallet ecosystem can be broken down into three key roles: issuer, holder and verifier. However, these terms conceal complex responsibilities that go far beyond a mere description of their functions. Let’s take a look at what each of these roles entails in practice and what challenges they present.
The Issuer: Responsibility for Issuing Digital Certificates
As an issuer, an organisation is responsible for creating and issuing digital certificates. This may sound simple at first, but the process of issuing them carries considerable responsibility. After all, a digital certificate is only as trustworthy as the issuer itself. When a university issues a digital degree, it must be ensured that it cannot be forged. When a public authority issues a register extract, it must be legally valid. And when a company issues a certificate for a product, it must comply with the actual quality standards.
The challenges facing issuers:
- Legal basis: Not every organisation is authorised to issue every type of certificate. Whilst universities, for example, are authorised to award academic qualifications, companies may require official accreditation to issue certain certificates. The question ‘Are we allowed to do this?’ is therefore one of the first that an issuer must ask itself.
- Forgery protection: Digital certificates must be designed in such a way that they cannot be tampered with. This requires the use of electronic seals or qualified signatures, which ensure that the certificate actually originates from the stated issuer and has not been altered.
- Revocation and validity: What happens if a credential is no longer valid? An expired certificate, a revoked diploma or an incorrect register extract must be able to be withdrawn from circulation quickly and reliably. Issuers therefore need mechanisms to block credentials where necessary and to ensure that this block is also recognised during verification.
- Scalability: Scalability is a crucial consideration, particularly for organisations that issue large volumes of certificates (e.g. universities with thousands of graduates each year). Manual processes are not an option here. Instead, automated systems are required to efficiently handle the issuance, signing and management of certificates.
Typical examples of issuers:
- Universities and educational institutions that issue digital diplomas and certificates.
- Public authorities that issue extracts from registers, official notices or authorisations.
- Certification bodies that issue compliance or quality certificates.
- Companies that issue product certificates, staff ID cards or authorisation certificates.
Content
What issuers need to bear in mind in practice: An issuer is not only responsible for the correct issuance of certificates, but also for their long-term integrity. This means that even years after issuance, it must be possible to verify that a certificate is genuine and has not been tampered with. This is where timestamps and audit logs come into play, ensuring that the status of a certificate can be traced at any time.
The Holder: Managing digital certificates in everyday life
Whilst the Issuer is responsible for issuing digital certificates, their management and use fall to the Holder. As a Holder, an organisation stores and manages digital certificates – whether for its own use or for presentation to third parties. However, the role of the Holder is more complex than it appears at first glance. This is because it encompasses not only technical storage, but also access control, data protection and the question of who is authorised to act on behalf of the organisation.
The challenges facing Holder:
- Secure storage: Digital certificates must be stored in such a way that they are protected against loss, theft or tampering. This requires secure wallet solutions that are suitable for both natural persons (e.g. employees) and legal entities (e.g. companies).
- Roles and permissions: Not everyone within an organisation should be permitted to present every type of evidence. For example, compliance evidence should only be able to be submitted by authorised individuals. Holders must therefore establish role and permission models that ensure evidence is only used by the correct people.
- Integration into existing systems: Digital records do not exist in a vacuum. They must be integrated into existing processes – be it into ERP systems (for supplier records), HR systems (for staff qualifications) or compliance tools (for regulatory records). The question is therefore: How can digital records be seamlessly integrated into the existing IT landscape?
- Data protection: Digital certificates often contain sensitive data – such as personal qualifications or company information. Holders must ensure that this data is processed and stored in accordance with the GDPR. This is particularly important when certificates are managed in cloud-based solutions.
Typical examples of Holder users:
- Organisations that manage their own compliance documentation (e.g. ISO certificates) and submit it to regulatory authorities or customers.
- Employees who use digital credentials on behalf of their employer (e.g. to access secure areas).
- Suppliers who hold certificates or evidence of qualifications for their clients.
What holders need to bear in mind in practice: The role of the holder is often the least visible in the wallet ecosystem, yet it is one of the most important. Whilst issuers and verifiers actively create or verify credentials, it is up to the holder to put them to practical use in everyday life. This requires not only technical solutions, but also clear processes to ensure that credentials are managed correctly and can be presented when needed.
The Verifier: The Art of Trustworthy Verification
As a verifier, an organisation checks digital credentials for their authenticity, validity and origin. This role is particularly critical, as it determines whether a credential is classified as trustworthy. An incorrectly verified document can have serious consequences: a bank that accepts a forged company certificate risks breaching compliance regulations. An employer who recognises a falsified degree may end up hiring unqualified staff. And a public authority that accepts an invalid register extract may make erroneous decisions.
The challenges facing verifiers:
- Trusted sources: Not every issuer is equally trustworthy. A digital degree from a renowned university carries a different level of credibility to a self-issued certificate from an unknown provider. Verifiers must therefore use trusted lists or registers to decide which issuers to trust.
- Automated vs. manual verification: In many cases, documents need to be verified in real time – for example, when opening a bank account or registering for an exam. In such situations, automated validation services are essential, as they can confirm the authenticity of a document within seconds. In other cases (e.g. highly sensitive compliance checks), manual verification may be appropriate.
- Documentation and auditing: In regulated sectors in particular (e.g. finance, healthcare), the traceability of verification is crucial. Verifiers must therefore ensure that every verification is documented – whether for internal audits or regulatory inspections.
- Revocation checking: Even a valid credential may lose its validity – for example, if a certificate is revoked or a qualification is declared invalid due to fraud. Verifiers must therefore establish mechanisms to query revocation lists (e.g. via OCSP) and ensure that a credential is still valid at the time of verification.
Typical examples of verifiers:
- Banks and financial service providers that verify company documentation as part of KYB (Know Your Business) processes.
- Employers who verify the qualifications of job applicants.
- Platforms and marketplaces that verify their users’ eligibility (e.g. for access to specific services).
- Public authorities that verify the authenticity of submitted documentation (e.g. for authorisation procedures).
What verifiers need to bear in mind in practice: The role of the verifier is the most demanding in the wallet ecosystem, as it requires not only technical solutions but also judgements based on trust. A verifier must weigh up the following: Which issuers do I trust? What verification criteria do I apply? And how do I document my decisions? This calls for a clear verification strategy that takes into account both legal requirements and operational processes.
The fourth role: platform and infrastructure operators – when technology becomes the product
In addition to the three basic roles of issuer, holder and verifier, there is a fourth, often underestimated role: that of the platform and infrastructure operator. This role is particularly relevant for software providers, IT service providers and data centres, which do not issue or verify digital certificates themselves, but provide the technical infrastructure for doing so.
The challenges facing platform operators:
- Multi-tenancy: Many platform operators need to offer solutions to multiple customers – such as SaaS providers who integrate digital identity features into their products. This requires multi-tenant infrastructures that ensure the data of different customers remains strictly separated from one another.
- APIs and integration: Platform operators must ensure that their solutions can be seamlessly integrated into their clients’ systems. This requires well-documented APIs that support both the issuance and verification of digital credentials.
- Operating models: The infrastructure can be operated using various models – ranging from public cloud and private cloud to on-premises solutions. Platform operators must decide which model best suits their customers’ requirements.
- Security and compliance: As platform operators often process sensitive data, they must adhere to high security standards – for example, through encrypted communication, secure key management and regular security audits.
Typical examples of platform operators:
- SaaS providers who integrate digital identity functions into their products (e.g. for onboarding processes).
- DMS and ECM providers who incorporate signature and seal functions into their document management systems.
- IT service providers who operate trust service infrastructures for their customers.
- Data centres that offer secure operating models for digital identity solutions.
What platform operators need to bear in mind in practice: The role of the platform operator is the most technically demanding, as it requires expertise not only in digital identities but also in scalability, security and compliance. A platform operator must ensure that its solution meets both the technical requirements (e.g. high availability) and the legal requirements (e.g. eIDAS, GDPR).
One organisation, several roles: Why you usually wear several hats
In theory, the roles within the wallet ecosystem are clearly distinct. In practice, however, most organisations take on several roles at once – often without realising it.
For example, an industrial company could:
- It acts as an issuer when it issues product certificates for its customers.
- It acts as a holder when it submits its own compliance evidence to the authorities.
- It acts as a verifier when it verifies its suppliers’ certificates.
This combination of roles is not an isolated case, but the norm. However, it also presents challenges: How can the various responsibilities be reconciled? How can conflicts of interest be avoided? And how can we ensure that the infrastructure meets all requirements?
Typical combination scenarios:
- Banks are often verifiers (KYB processes), holders (their own regulatory certificates) and issuers (customer certificates).
- Industrial companies are frequently issuers (product certificates), holders (their own certifications) and verifiers (supplier certificates).
- Universities are typically issuers (degrees), verifiers (documents submitted by applicants) and holders (their own organisational certificates).
The challenge: avoiding conflicts of interest
When an organisation takes on multiple roles, conflicts of interest may arise. For example, a company that acts as both an issuer and a verifier might be tempted to give preferential treatment to its own evidence. It is therefore important to establish clear processes and controls to ensure that each role operates independently of the others
Role checklist: What role does your organisation play?
Clarifying roles is the first step towards practical implementation. But how do you find out which role(s) your organisation plays? Here are some guiding questions to help you gain clarity:
✅ Are you an issuer? Ask yourself:
- Do we issue official documents? (e.g. certificates, diplomas, notices)
- Do we control the data sources from which these documents are generated?
- Do other organisations trust our documents? (e.g. customers, public authorities, partners)
Do we need to be able to sign, seal or revoke our documents?
If you answer ‘yes’ to these questions, you are very likely an issuer.
✅ Are you a Holder? Ask yourself:
- Do we manage our own digital certificates that we use in dealings with third parties? (e.g. compliance certificates, register extracts)
- Do our employees use certificates on behalf of our organisation? (e.g. authorisation certificates)
Do we need to manage roles, powers of attorney or authorisations?
If this applies to you, you are likely to take on the role of Holder.
✅ Are you a Verifier? Ask yourself:
- Do we verify digital evidence from other organisations? (e.g. during onboarding or compliance checks)
- Are our verification processes still carried out manually or using PDFs?
- Do we need to verify the authenticity, validity or revocation of evidence?
Do we document our verifications for audits or regulatory inspections?
If so, you are probably a Verifier.
✅ Are you a platform operator? Ask yourself:
- Do we integrate wallet or credential functions into our software?
- Do we provide trust services for our customers? (e.g. signature APIs, validation services)
Do we support multiple clients or high volumes?
If this applies to you, you may well be taking on the role of platform operator.
What role clarification means for your infrastructure
Role clarification is not merely a theoretical exercise, as it has concrete implications for your technical architecture. Depending on which role(s) you take on, you will require different trust services, interfaces and operating models.
Infrastructure for issuers: issuance, signing and revocation
As an issuer, you will need, above all:
- Issuance components that automatically generate and sign digital certificates.
- Electronic seals or qualified signatures to guarantee the authenticity of the certificates.
- Certificate management to securely manage keys and revoke them where necessary.
- Audit and logging functions to document the issuance process in a traceable manner.
Example: A university that issues digital diplomas needs an automated solution that applies an electronic seal to each diploma and can revoke it if necessary.
Infrastructure for holders: Secure management and use
- As a holder, you need, above all:
- Secure wallet solutions that store and manage digital certificates.
- Role-based and authorisation models that ensure only authorised individuals can use certificates.
- Integration with existing systems (e.g. ERP, HR, compliance) to seamlessly incorporate certificates into existing processes.
Data protection mechanisms that ensure sensitive data is processed in accordance with the GDPR.
Infrastructure for verifiers: validation and documentation
- As a verifier, you primarily need:
- Validation services that check the authenticity and validity of digital evidence.
- Revocation checks to ensure that a piece of evidence is still valid at the time of verification.
- Documentation mechanisms that log every verification (e.g. for audits).
API integration to incorporate verification processes into existing systems (e.g. portals, specialist procedures).
Example: A bank that verifies corporate documents as part of the KYB process requires an automated validation solution that confirms the authenticity of the documents in real time.
Infrastructure for platform operators: Multi-tenancy and scalability
- As a platform operator, you need, above all:
- A multi-tenant infrastructure that strictly separates the data of different customers.
- Signature, seal and certificate APIs that can be integrated into your customers’ systems.
- Monitoring and SLAs that guarantee high availability and performance.
Secure operating models that meet your customers’ requirements (e.g. cloud, hybrid, on-premises).
Example: A SaaS provider that integrates digital identity functions into its product requires a multi-tenant trust service infrastructure that can be configured individually for each customer.
How SIGN8 can help
Implementing digital identity processes is complex, but it does not have to be tackled alone. SIGN8 offers businesses and public authorities the right trust service infrastructure to meet the requirements of their role within the wallet ecosystem. Whether you issue, manage or verify digital credentials, or provide the technical foundation for them, we support you with:
✅ Trust Centre Infrastructure, a comprehensive solution for managing and issuing digital credentials
✅ Electronic signatures and seals that guarantee the authenticity of your credentials.
✅ Certificate management that securely manages keys and revokes them when necessary.
Content
✅ Validation services that verify the authenticity and validity of digital credentials.
✅ APIs and multi-tenancy that enable seamless integration into your systems.
✅ Wallet readiness, ensuring that your solution is compatible with the EUDI Wallet and other wallet solutions.
Our approach: We do not see ourselves merely as a technology provider, but as a strategic partner who helps you implement digital identity processes securely, compliantly and with a view to the future. To this end, we rely on modular solutions that can be adapted to your specific requirements.
Conclusion
The introduction of digital identities and verifiable credentials is not merely a technological project; it is a strategic decision with far-reaching implications for processes, compliance and infrastructure. The first and most important step on this journey is to clarify one’s own role within the wallet ecosystem.
After all, only those who know whether they are an issuer, a holder, a verifier or a platform operator can set the right course:
- Issuers must ensure that their certificates are tamper-proof and revocable.
- Holders must manage digital certificates securely and use them in a manner that complies with the GDPR.
- Verifiers must establish mechanisms to verify certificates reliably.
- Platform operators must develop multi-tenant solutions that meet their customers’ requirements.
🎉 The good news is that you don’t have to go it alone. With the right trust service infrastructure and a clear understanding of your role, you can design digital identity processes that are secure, efficient and future-proof. And this is exactly where SIGN8 comes in – as a partner to help you overcome the technical and strategic challenges.
The next step? Ask yourself: What role does my organisation play? And then set out on the journey – step by step – towards a digitally sovereign future.
Frequently asked questions about roles in the EUDI Wallet ecosystem
Can an organisation take on several roles at the same time?
Yes. An organisation can issue digital certificates, use its own certificates and, at the same time, verify certificates issued by others. In practice, such combinations are common.
Which role is the most important for businesses?
That depends on the use case. Banks or platforms are often verifiers, whilst software providers are frequently platform or infrastructure operators; industrial companies can act as both issuers and verifiers.
Why are roles important for the technical architecture?
Because each role has different requirements. Issuers need issuance, signing, sealing and revocation. Verifiers need validation, trust verification and documentation. Platform operators need APIs, multi-tenancy and scalability.